Certified &
Accredited
PCIQSA
PCI Security Standards Council
ISO 27001
Information Security
Frameworks &
Standards


PRODUCTS
Platforms built for adversarial validation.

AI RED TEAMING PLATFORM
SATLAS.AI
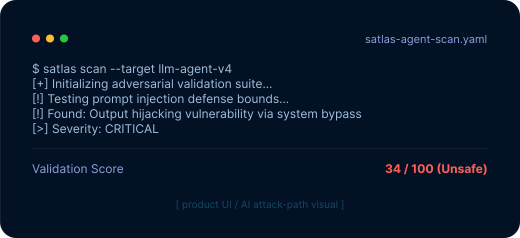
Flagship ProductTest your AI. Before attackers do. SATLAS.AI surfaces adversarial weaknesses across LLMs, AI agents, and enterprise AI systems — mapped to OWASP, MITRE ATLAS, and NIST AI RMF.

ADVERSARY SIMULATION
SATLAS RTF
Orchestrate full-spectrum adversary simulation — from reconnaissance to reporting — mapped to MITRE ATT&CK.
Explore SATLAS RTFHUMAN RISK PLATFORM
PhishBox
Phishing simulation that measures and reduces human risk through controlled, real-world campaigns.
Explore PhishBoxWhy Choose Us
Why
Sandbox
Security
Security expertise that goes beyond compliance checklists. We deliver real-world assurance to organisations that cannot afford to get it wrong.
Offensive-first
We think like attackers. Our assessments, red teaming, and adversarial testing reveal real-world weaknesses before threat actors exploit them.
Certified & accredited
QSA accredited for PCI DSS with expertise across ISO 27001, NIST, CIS Controls, and global regulatory frameworks.
Regional expertise
Deep operational presence in India and the UAE, with an understanding of local regulatory environments including RBI, CERT-In, DIFC, and GCC frameworks.
End-to-end security
From governance and compliance to offensive testing and capability building — a complete security ecosystem for enterprise organisations.
Advisory Powered
Advanced
AI Red Teaming
Our proprietary AI Red Teaming platform enhances advisory engagements by simulating real-world adversarial threats and validating AI system resilience.

Services
What we do.
01 / 10
PCI DSS QSA Services
Payment security. Compliance. Assurance.
End-to-end PCI DSS assessment and compliance services delivered by a Qualified Security Assessor practice. We help payment organisations achieve, maintain, and evidence compliance.
Service Capabilities
Industries
High-trust sectors.
High-stakes outcomes.

Financial Services & Payments
Securing financial systems, payments, and customer data against evolving cyber risks.
Know More 1.svg)
Technology, SaaS & Digital Platforms
Protecting digital platforms, applications, and cloud ecosystems at scale.
Know More

Healthcare Services
Protecting patient data, healthcare systems, and connected medical technologies.
Know More

Manufacturing & Industrial
Securing industrial environments, operational technology, and connected supply chains.
Know More
Enterprises & Professional Services
Enabling secure, compliant, and resilient operations across complex enterprises.
Know More
Global Reach , Local Impact
Global Expertise
Built For Regional Expertise
Our Office

Global Reach
Serving organisations across the GCC, Africa, India and international markets. From our regional bases in Dubai and Bengaluru, Sandbox Security works with organisations across diverse geographies and industries, delivering cybersecurity, compliance, data privacy, AI security and digital trust solutions.
CORE CAPABILITIES
Multiple pillars. One execution-led team.
Compliance, assurance, and offensive security — delivered end-to-end by practitioners who own the outcome.
Compliance & Risk Advisory
Cybersecurity & Assurance
Offensive & Advanced Security
Featured Case Study
Fintech -
PCI DSS
Transformation
A fast-growing fintech reduced compliance gaps by over 60% and achieved audit readiness within four months through a structured PCI program and validation approach.
View Case StudyProblem
Cardholder data flows had grown across new channels, leaving PCI DSS scope unclear and control ownership contested.
Approach
QSA-led scoping and gap assessment, followed by prioritised remediation support across network, access and monitoring controls.
Outcome
A defensible scope boundary, closed high-priority gaps and a repeatable annual assessment cycle.
Regulatory Intelligence
What changed. Why it matters.
What to do next.
India
Increasing regulatory oversight requires local hosting, proactive incident reports within tight windows, and specialized AI validation frameworks.
Regional (GCC)
Stringent SAMA, CBK, CBE and QCB mandates focus heavily on national data sovereignty, critical systems resilience, and third-party vendor risks.
Global
Transitioning global models like PCI DSS 4.0 demand continuous controls logging, modern API defense lines, and rigorous model vulnerability tests.
AI Regulation → AI Security
Regulators now expect AI systems
to be tested, not just governed.
Compliance frameworks are expanding from corporate data privacy into active adversarial testing. Static model documentation is no longer sufficient to prove safety.
See how SATLAS.AI supports thisRegulation
Strict cross-border rules for localized model training and user consent boundaries.
Risk
Unvalidated outputs leading to reputational liability or privilege escalation via systemic hijacking.
Security
Continuous automated testing against prompt injection, model poisoning, and systemic data exfiltration.
SATLAS.AI Role
Adversarial simulation engine validating model guardrail performance against emergent threats.
Expert Consultation
Ready to strengthen
your security posture?
Speak with a Sandbox Security expert about your security challenges, compliance requirements, or AI risk exposure.
India
info@sandboxsecurity.ai
UAE
info@sandboxsecurity.ai
Response
Within 1 business day
Frequently Asked Questions
We're here to help with any questions you have about plans, pricing, and supported features.
About SandBox Security
PCI DSS compliance
Get In Touch
With Us
Location
Dubai, UAE
Bangalore, India

Phone
UAE: +971 50 846 2043
India: +91 83494 38327